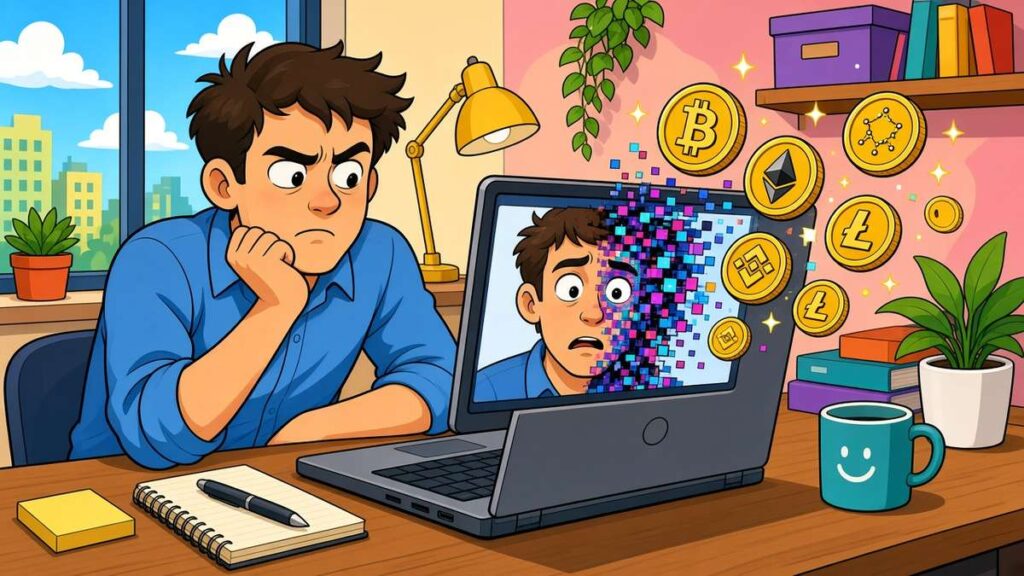
The Colleague on the Call Isn’t Really There: How North Korea’s ‘FaceStealer’ Turned Webcams Into a $400 Million Heist
The trick works because nothing about it feels like a trick. A message arrives from someone you know — a former collaborator, a developer from a project you contributed to. They suggest a quick video call. When you join, there they are on screen, nodding, apparently talking. Only the sound seems broken.
That small glitch, according to the US Federal Bureau of Investigation, is where one of North Korea’s most effective hacking operations of recent years begins. The bureau says state-backed hackers using a scheme it calls “FaceStealer” have taken more than $400 million in cryptocurrency over the past 18 months, with more than 900 people caught in the net.
How the loop works
The FBI and the US Justice Department describe a cycle that feeds itself:
- The invitation. Using fake or hijacked social media accounts, the attackers invite a target to a meeting on what look like familiar platforms — but are actually imposter versions of Zoom, Microsoft Teams or Google Meet.
- The borrowed face. Instead of a live person, the target sees pre-recorded footage of a previous victim, ideally someone they already know. To hide the fact that the “speaker” cannot respond, the audio appears to fail.
- The fix. A pop-up offers to repair the sound. Clicking it eventually installs malware that opens up the victim’s device, including their contacts and apps.
- The recording. The call itself is secretly recorded. The new victim’s face becomes raw material for fooling the next person on their contact list.
Each success therefore produces both money and fresh bait. The FBI says it has seized more than 900 such recorded victim videos — an unsettling archive of ordinary people in front of their webcams, repurposed as disguises.
Who is being targeted
The scheme focuses on people working in cryptocurrency and Web3, especially those who build and maintain open-source software. That makes sense from an attacker’s point of view. Open-source communities run on trust between people who often know each other only through screens, and a single compromised maintainer can provide access to wallets, code repositories or a whole network of collaborators.
FBI officials have been unusually frank about how hard this is to spot. The bureau described FaceStealer as capable of deceiving even experienced, security-conscious technical users. One senior agent in Los Angeles put it more memorably: if you can’t imagine a scenario in which you would fall for it, you are not thinking creatively enough.
Why it matters beyond crypto
US officials say Pyongyang relies heavily on large-scale crypto theft to fund its weapons programmes, and the FaceStealer disclosure comes only a week after Binance said hackers had used fake job interviews to take a record $6.3 billion from the exchange — an attack US agencies attributed to North Korea-linked actors. North Korea has denied involvement.
The broader lesson is about video itself. For years, seeing someone’s face on a call has served as informal proof of identity. FaceStealer exploits exactly that habit, and it does not even require sophisticated deepfakes: real recordings, played at the right moment, are enough.
Practical takeaways
Security teams are likely to repeat a few simple rules in the coming weeks. Treat any meeting link that doesn’t come from an official domain with suspicion. Never install software to “fix” audio or video during a call. If a familiar face seems unable to respond, confirm through a separate channel before going further. None of this is new advice. What is new is the price of ignoring it.